201 CMR 17.00 is the Massachusetts rule requiring any business that holds personal information on a Massachusetts resident to keep a written information security program, or WISP. That includes car dealerships wherever they sit, and it covers employee records too.
Last updated: November 3, 2026
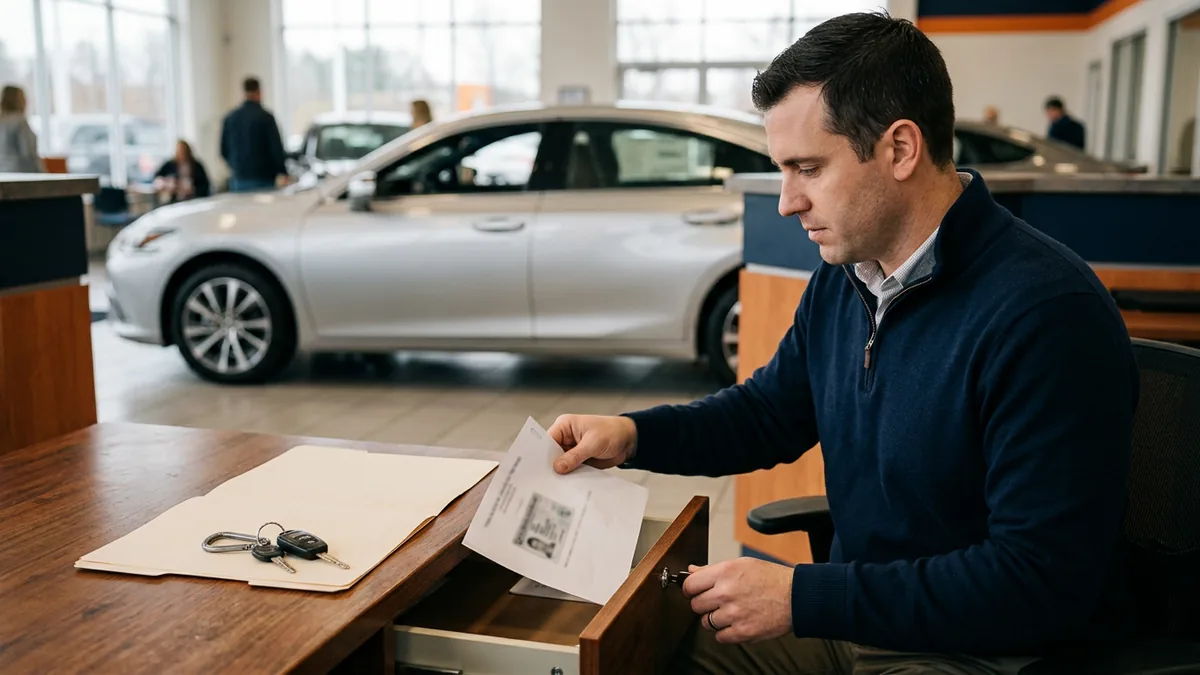
Somewhere on your sales desk there’s a photocopy of a driver’s license. It’s probably clipped to a test-drive form. It’s probably in a drawer that doesn’t lock.
Under Massachusetts law, that copy is personal information. A name plus a license number. That’s all it takes.
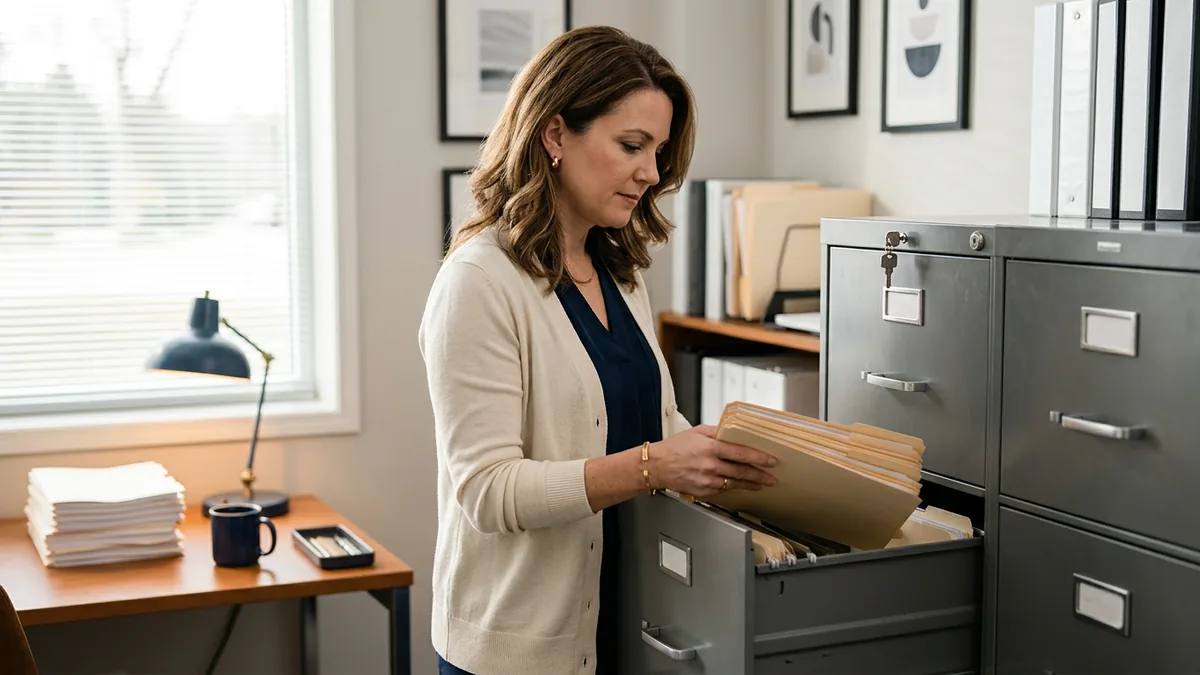
Down the hall, the office manager keeps a payroll file with every technician’s Social Security number in it. Same rule covers it. And here’s the part that surprises dealers who already did their FTC Safeguards Rule work: the federal rule never asked about that payroll file. Massachusetts does.
I’ve worked in most of the chairs in a dealership, from writing service to parts to accounting, and later spent years building training for dealership staff on the software side. The accounting chair is where this regulation lands hardest. It’s also where a good program pays off fastest, because the same habits that protect a deal jacket protect a W-4.
Massachusetts sits in an odd spot on our map of dealership privacy laws by state. There’s no consumer privacy law in force there as of this writing, though a bill has been working through the legislature. The security rule has been on the books since 2010. That one matters today.
What 201 CMR 17.00 Actually Requires
201 CMR 17.00 is a Massachusetts regulation, issued by the Office of Consumer Affairs and Business Regulation under Chapter 93H, that sets minimum standards for protecting residents’ personal information. Anyone who owns or licenses that information must keep a written information security program with administrative, technical, and physical safeguards.
It took effect March 1, 2010. You can read the full text on the state’s regulation page.
Two definitions do most of the work. “Personal information” means a Massachusetts resident’s first name or first initial and last name, combined with a Social Security number, a driver’s license or state ID number, or a financial account, credit, or debit card number. “Owns or licenses” means you receive, store, process, or have access to that information in connection with selling goods or services, or in connection with employment.
Now run that against a normal week at a store, and you’ll find it everywhere: the credit application in F&I, the license copy at the test-drive desk, the card number the cashier keys in for a brake job, and the direct deposit form a new porter fills out on their first morning before anyone has even shown them where the coffee is.
All of it counts.
Sitting across the state line doesn’t help, either. The rule rides along with the customer rather than the building, so if your store is in Salem, New Hampshire, or Pawtucket, Rhode Island, and a good share of your buyers drive in from Massachusetts, the files you keep on them are Massachusetts files under this regulation.
Easy to miss.
Where 201 CMR 17 Asks for More Than the Safeguards Rule
If you finance or lease, you’re already living under the FTC Safeguards Rule, and the FTC’s own Safeguards Rule FAQ for auto dealers spells out why. What Massachusetts piles on top of that is more than most people expect when they first sit down with the two rules, so here they are side by side.
| Topic | FTC Safeguards Rule | 201 CMR 17.00 |
|---|---|---|
| Whose data | Customer information | Customers and employees who are Massachusetts residents |
| Small-store relief | Under 5,000 consumers skips the written risk assessment, pen testing, incident plan, and board report | No carve-out. Every element applies, scaled to your size |
| Discipline | Not spelled out | Required for violations of the program |
| Departing employees | Covered by general access controls | Must be blocked from records containing personal information |
| Paper records | Physical access controls | Kept in locked facilities, storage areas, or containers |
| After an incident | Written incident response plan; FTC notice for events involving 500 or more consumers | Documented response plus a mandatory post-incident review of what changed |
| Breach notice | To the FTC within 30 days of discovery | To the attorney general and the consumer affairs office, stating whether you keep a WISP |
I’d start with the employee row, since it’s the one that changes the most work for the office. The federal rule was written around the customer sitting in your F&I office, so the technician’s I-9 and the salesperson’s direct deposit slip were never its concern, and neither was the benefits form with a spouse’s Social Security number on it. Massachusetts folds all of those into your program, which puts your HR folders, the payroll export, and whatever outside company runs payroll for you on the same footing as a deal jacket.
They always belonged there.
The small-store row trips up single-point dealers. Under 16 CFR 314.6, a dealer with customer information on fewer than 5,000 consumers is excused from four federal elements, including the written risk assessment and the incident response plan. Massachusetts has no matching exception. None at all. A smaller store can keep its program simpler, since the rule scales to your size and resources, but it still has to assess risks and document how it handles an incident. Smaller isn’t exempt.
Then there’s the breach notice. Since a 2019 change to Chapter 93H, a notice to the attorney general and the Office of Consumer Affairs and Business Regulation has to say whether you maintained a written information security program at the time. If Social Security numbers were exposed, you also have to offer affected residents at least 18 months of free credit monitoring. The state’s page on notifications in the event of a data breach walks through it.
Think about that question on the form for a second. Did you have a WISP? It’s a yes-or-no box.
You want to check yes.
Where the Safeguards Rule Asks for More
It cuts both ways. On the technical side, the federal rule is stricter, and by a fair margin.
Massachusetts asks you to encrypt personal information that crosses public networks, anything sent wirelessly, and anything stored on laptops or other portable devices, all “to the extent technically feasible.” The Safeguards Rule asks you to encrypt all customer information you hold or send, at rest and in transit over external networks, with exceptions only where your Qualified Individual approves compensating controls. It requires multi-factor authentication for anyone accessing any information system. It requires a named Qualified Individual who reports to your board or owner in writing at least once a year, plus annual penetration testing and vulnerability scans every six months unless you run effective continuous monitoring. It also wants customer data disposed of no later than two years after you last used it, with some exceptions. Our breakdown of the nine Safeguards Rule requirements covers each one, and the text sits in 16 CFR 314.4.
That’s a long list. So neither rule is the bigger one. Massachusetts is wider. The FTC is deeper.
One Program That Covers Both
Here’s how I’d explain it to a used-car manager. A certified pre-owned car still needs its state inspection sticker. Two checklists, one car, and nobody reconditions it twice. You do the recon once, to the tougher standard on each item, and both inspectors sign off.
A WISP works the same way. Build to the Safeguards Rule’s technical floor, widen the scope to Massachusetts’s definition, and you have one program instead of two binders that disagree with each other. Our dealership WISP template is a good starting frame. For a Massachusetts store, these are the additions I’d make to it:
- Add employee records to the inventory of what you hold. Payroll, HR, benefits, and the folder of license copies from new-hire paperwork.
- Write a discipline clause into the program and the employee handbook. One sentence is fine, as long as it’s real and people sign it.
- Tie IT to HR on terminations so the DMS login, email, and building access all close the same day someone leaves. Same day, not same week.
- Lock the paper. Every drawer, cabinet, or room where deal jackets, license copies, and payroll files live.
- Add a post-incident review step to your incident response plan template, so every incident ends with a written note on what changed in the business.
- Put the Massachusetts notice and credit-monitoring steps into the breach section, next to the FTC breach notification steps.
- Set the annual review date on the calendar, and set a trigger for an earlier review after any material change, like adding a store, switching a payroll vendor, or opening a collision center.
That’s the real work. None of it is exotic. It’s mostly paperwork and habits.
What It Looks Like for the People on the Floor
A WISP that sits in a binder in the GM’s office doesn’t protect much on its own, which is why the regulation asks for ongoing employee training and regular checks that the program is actually working. Here’s what that looks like desk by desk.
| Where | The habit | Why Massachusetts cares |
|---|---|---|
| Test-drive desk | The license copy goes into a locked bin after it’s scanned, not a folder by the keyboard | Name plus license number is personal information, and paper has to be locked up |
| F&I office | No credit apps emailed to a personal account to finish deals at home | Personal information crossing a public network has to be encrypted |
| Service write-up counter | Card numbers never get read back out loud with a line of customers waiting | A card number with a name is personal information |
| Accounting | The payroll file for the outside CPA goes on an encrypted drive or a secure transfer, never a plain thumb drive | Personal information on portable devices has to be encrypted |
| Sales manager and HR | A departing salesperson’s DMS login, email, and door code close the day they leave | Terminated employees must be blocked from records |
Accounting is the one I’d watch. The thumb drive habit usually started years ago because it was easy, and nobody meant any harm by it, but workarounds need to be left in the past.
Training is the other half. At the Cleveland Auto Show a while back, a couple of brands kept their cars locked, display only, and I thought it was a missed chance, because people come to a show to sit in the seat and get a feel for the thing. Your people learn the same way. Walk the desk with them, open the drawers together, and ask the cashier where the card slips go until nobody has to think about the answer.
Across the 2,000-plus dealerships we support, the written program is rarely the missing piece.
The habit at the desk is.
If you have stores across New England, our Boston dealership IT services page puts Massachusetts next to its neighbors. And if you’d rather have one team keep the program current, the scans run, and the evidence ready, that’s what our continuous compliance program for dealerships is built to do.
Questions Massachusetts Dealers Ask Us
Our store is in New Hampshire. Does a Massachusetts rule really reach us?
Is a WISP just our Safeguards Rule program with a new name?
Payroll and HR files too, or only customer deals?
We had an incident with Massachusetts customers in it. Who hears about it?
Realistically, how often does the WISP get reviewed?
I spent years building training for dealership staff before I came to Helion Technologies, and the thing I believe most from that work is that people keep what they practice. A WISP is no different. Build one program to the tougher standard on every line, walk it with your team, and look at it again whenever the store changes, and a Massachusetts store is set up for success under both rules.
If you’d like a second set of eyes first, our complimentary IT and cybersecurity assessment will show you which pieces are already in place and which ones are still sitting in a drawer.